
Penetration Testing | Ascot
Penetration Testing in Ascot
Penetration testing in Ascot carried out by a human tester. We try your firewall, VPN, Wi-Fi, website and Microsoft 365 sign-ins the way an intruder would, then list fixes by urgency.
Test my systemsTrusted pen testing, industry certified.


What a pen test is
An Agreed Attack, Not a Real One
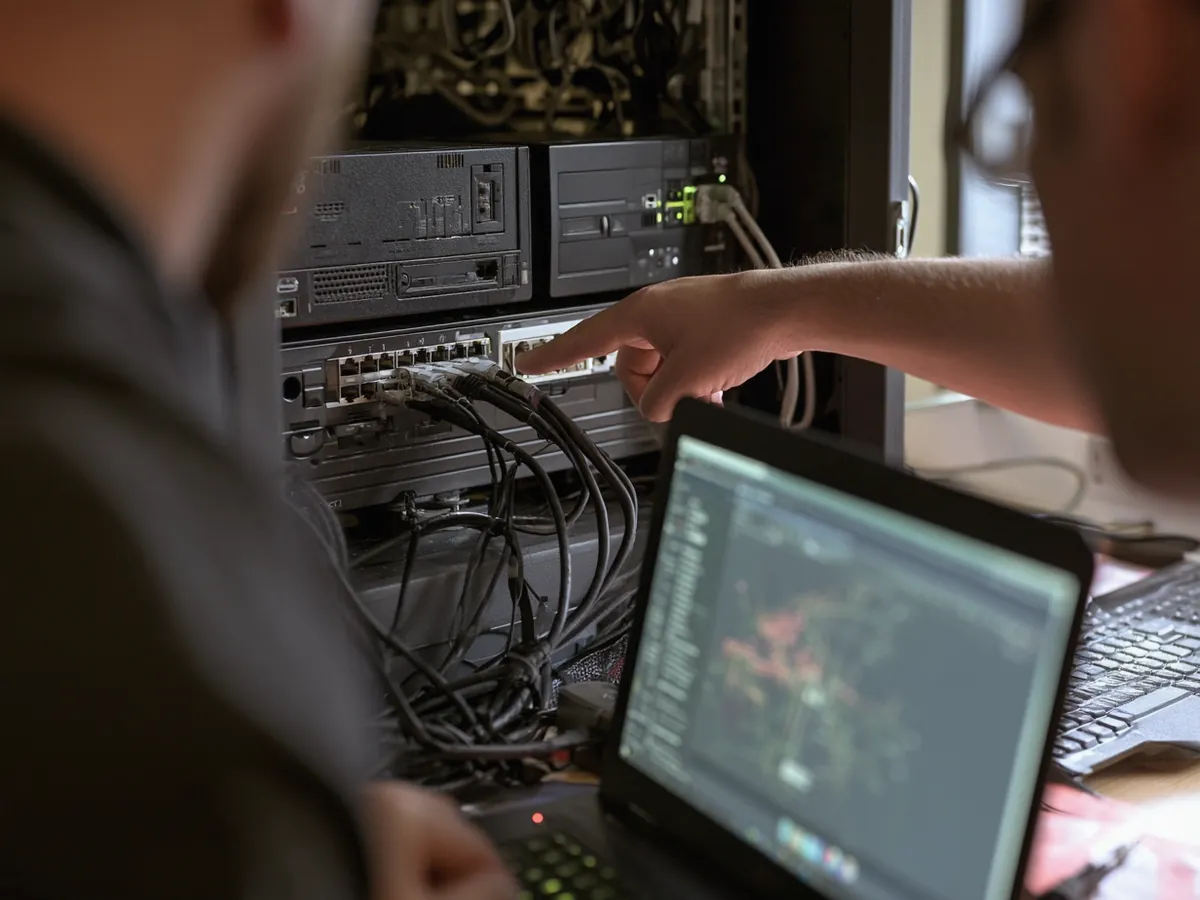
Pen testing means paying someone to attack you on purpose, with your written permission and inside limits you set. Our tester points real attack tools at your internet line, remote access, public website, wireless network and user accounts. A vulnerability scan says what might be weak. A pen test shows what an outsider could genuinely get into, and how far.
Firms on Ascot High Street, in Sunninghill and Sunningdale ask for one when they hold client records, take payments online, offer visitor Wi-Fi or plan for Cyber Essentials Plus.
Typical first-test findings
- Remote desktop open to the internet behind one weak password
- An old website plugin that leaks records to a crafted request
- Visitor Wi-Fi that can see the same network as the file server
- An insurer or client wanting test results you cannot yet show
Test types
Penetration Tests Sized for Ascot Firms
Scanners produce long lists of maybes. A tester confirms which items can actually be used against you and explains each fix in everyday language, in order of how much harm it could do.
External infrastructure test
From outside your building we go after your firewall, VPN, remote desktop, mail servers and public IP ranges, taking the same route a stranger on the internet would take.
Internal network and wireless
On site we connect to your network, try the staff and visitor Wi-Fi and see how far one compromised laptop could reach.
Web apps and portals
Your website, enquiry forms and client log-in areas are checked for injection, weak sessions and leaking data.
Findings in order of risk
Every issue gets a rating, evidence and the steps to fix it. Owners get a single summary page; your IT team or provider gets the full technical write-up.
Retesting after your fixes
Once the work is done we test those items again and confirm each one is shut, so you have evidence to show clients and insurers.
First test vs retest
How a Pen Test Changes an Ascot Network
Nobody notices a weakness until someone goes hunting for it. Below are common findings from a first test and where they stand once the retest is done.
| Area | First test | After the retest |
|---|---|---|
| Remote access | VPN running firmware with a known flaw. | Rated critical, patched first and tested again. |
| Web forms | One form shows other people's details. | Corrected, retested and confirmed for clients. |
| Local admin | One admin password shared across PCs. | A different admin password per PC, behind MFA. |
| Guest Wi-Fi | Visitors can open office shared folders. | Visitors on their own network, checked by test. |
Our method
Agree, Attack, Explain, Then Check Again
We put the targets, dates and permitted techniques in a signed scope before anything is touched. Testing fits around your working day, you get progress updates, and we halt straight away if a live service or your staff are being affected.
Agree: targets and rules
Together we list the IP ranges, sites, premises and accounts in scope, fix the dates and the rules of engagement, and record the lot in a signed document.
Attack: try each weakness
Automated scanning gives a starting list. Our tester then works each item manually to learn how deep an attacker could go.
Explain: the written report
The report scores each finding, includes proof and sets out the fix. We walk through it on a call with your owners and the person or company that runs your IT.
Check again, then annually
When fixes are in we retest to prove them. Testing once a year, and again after any large change, keeps the results up to date.
Penetration testing FAQs
Penetration Testing in Ascot: Common Questions
How do you price a pen test?
The scope. We look at how many public IP addresses, websites, sites and user accounts are involved, and whether you want an internal test on your premises as well as the external one. You get a fixed written quote before we book dates, and it stays the same once testing begins.
Can vulnerability scanning replace a pen test?
Not on its own. A scanner reports known issues and raises plenty of false alarms. A human tester sorts real problems from noise, links weaknesses together and shows exactly what an attacker would reach. Scanning between tests is worth doing, but it is a different job.
Will testing disrupt our staff?
It should not. You agree the testing windows, we check with you before anything that might touch a live system, and we stop at once if something is affected. Most people in the office never notice it happening.
Does a pen test count as Cyber Essentials Plus?
No. Cyber Essentials Plus is a certified assessor auditing five fixed controls. A pen test goes further, and fixing what it finds leaves you better prepared for that audit.
What if you find something serious?
We tell you on the day rather than saving it for the report. If data is exposed right now, we give you an interim fix and can put it in place, then carry on with the rest of the scope. Ring 01344 233339 to discuss it.
How regularly should we be tested?
Once a year suits most firms, with an extra test after big changes such as a new firewall, a website rebuild, moving office or moving to the cloud. Some clients and insurers set their own timetable, so check your contracts.
Do you test businesses around Ascot too?
Yes. We test firms in Sunninghill, Sunningdale, South Ascot, North Ascot, Cheapside and Winkfield. External testing is remote, and internal testing happens on site.
Get in touch
Book Penetration Testing in Ascot
Let us know what you want tested, from a single website to a full office network, and we will scope it and send a fixed quote. Call 01344 233339, email hello@ascotitsupport.co.uk or send the form; most messages get a reply within the hour.
Contact us